

Wow! I once left a coin on an exchange and felt gut-punched the next morning. My instinct said ‘do not trust one custodian’ and that feeling stuck. NFC backup cards let you carry your keys in a thing that behaves like a credit card while keeping the private key offline, which sounds almost too neat. Seriously?
They aren’t just fancy trinkets; they’re audited devices meant for secure signing. Most use secure elements and a tamper-resistant design to protect seeds. On one hand this gives convenience—tap your phone, sign a tx—though actually security depends on the implementation and the backup strategy. Initially I thought a single card was enough, but then realized redundancy matters. That reality forces you to think about recovery procedures.
Here’s the thing. If your card uses a certified secure element and never exposes the private key, it’s much safer than a hot wallet. But not every NFC card is created equal; check audits and sourcing. Validate the chipset, check the supply chain, read audits, and prefer open designs when possible. I’m biased, but I favor solutions that combine on-card signing with an offline backup plan.
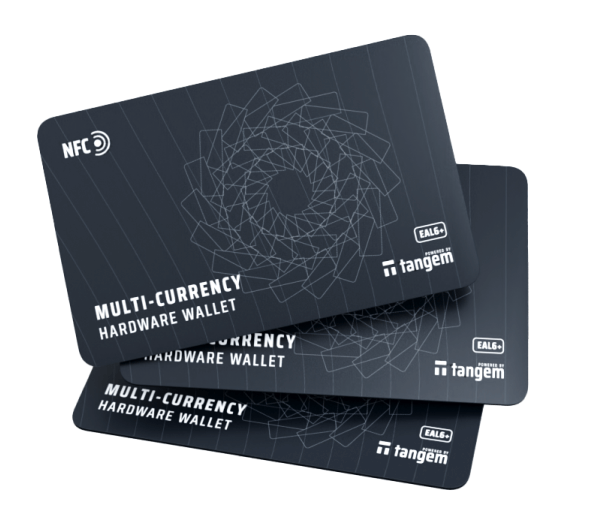
A practical checklist before you tap
Wow! Backup cards can be your cold storage and your last-resort recovery method all rolled into one. The common pattern uses a sealed secure element that holds the private key and an NFC interface that performs signing without exporting the key. Still, decide how you’ll back up the card itself; it’s very very important. For many users a secondary card stored separately is a good tradeoff.
Really? Consider also how you’ll manage firmware updates and whether the manufacturer supports verifiable updates. On one hand constant updates are good for security, though actually they introduce supply-chain complexity and trust decisions you must make. Check community threads and professional reviews before committing to any irreversible purchase; somethin’ to watch. I’m not 100% sure any single approach fits everyone, but if you pair an NFC backup card with a robust recovery plan — multi-card backups, geographically separate storage, or complementary hardware wallets — you get a resilient system that balances convenience and security…
Okay, so check this out—I’ve been using a mix of device types for years, and the tactile ease of tapping a card to sign in a crowded cafe still feels unreal. Whoa! It speeds mundane ops without leaking keys. That said, if the supply chain is sketchy or the firmware opaque, you trade one risk for another. I’m cautious about single-vendor black boxes, though actually vetted secure elements can be fine for everyday holdings.
One practical example: I use an offline card for small to medium values that I need to move occasionally, and a multisig setup for the rest. It reduces friction while keeping higher-value holdings under stronger, slower-to-access controls. (oh, and by the way…) if you travel, think about customs and local laws; physical crypto devices sometimes raise eyebrows at borders.
FAQ
What happens if I lose the NFC card?
If you lose a card, recovery depends on your backup plan. Ideally you’ve stored a secondary card or a split-seed backup in separate locations. Some users write down recovery phrases, others use Shamir or multi-card schemes. Initially I thought a single paper seed was enough, but redundancy matters more than I expected.
Are all NFC cards recommended for cold storage?
No. Only cards with secure elements and proper on-card signing should be used for cold storage. Check for audits, reputable manufacturers, and a clear update path. I’m biased toward open designs or at least well-documented implementations like the ones community vets.
Any vendor you can point to?
If you’re browsing options, one place people often look at is tangem, which emphasizes card-like hardware and secure elements in their product line; read up on audits and community feedback before you commit.

Lascia un commento